Researchers describe a Muse security chain they say was fixed before disclosure
NebuSec published a report describing how an attacker-controlled webpage could expose private information inside a Muse user's environment. The researchers say all exploits they describe were patched before publication.
What
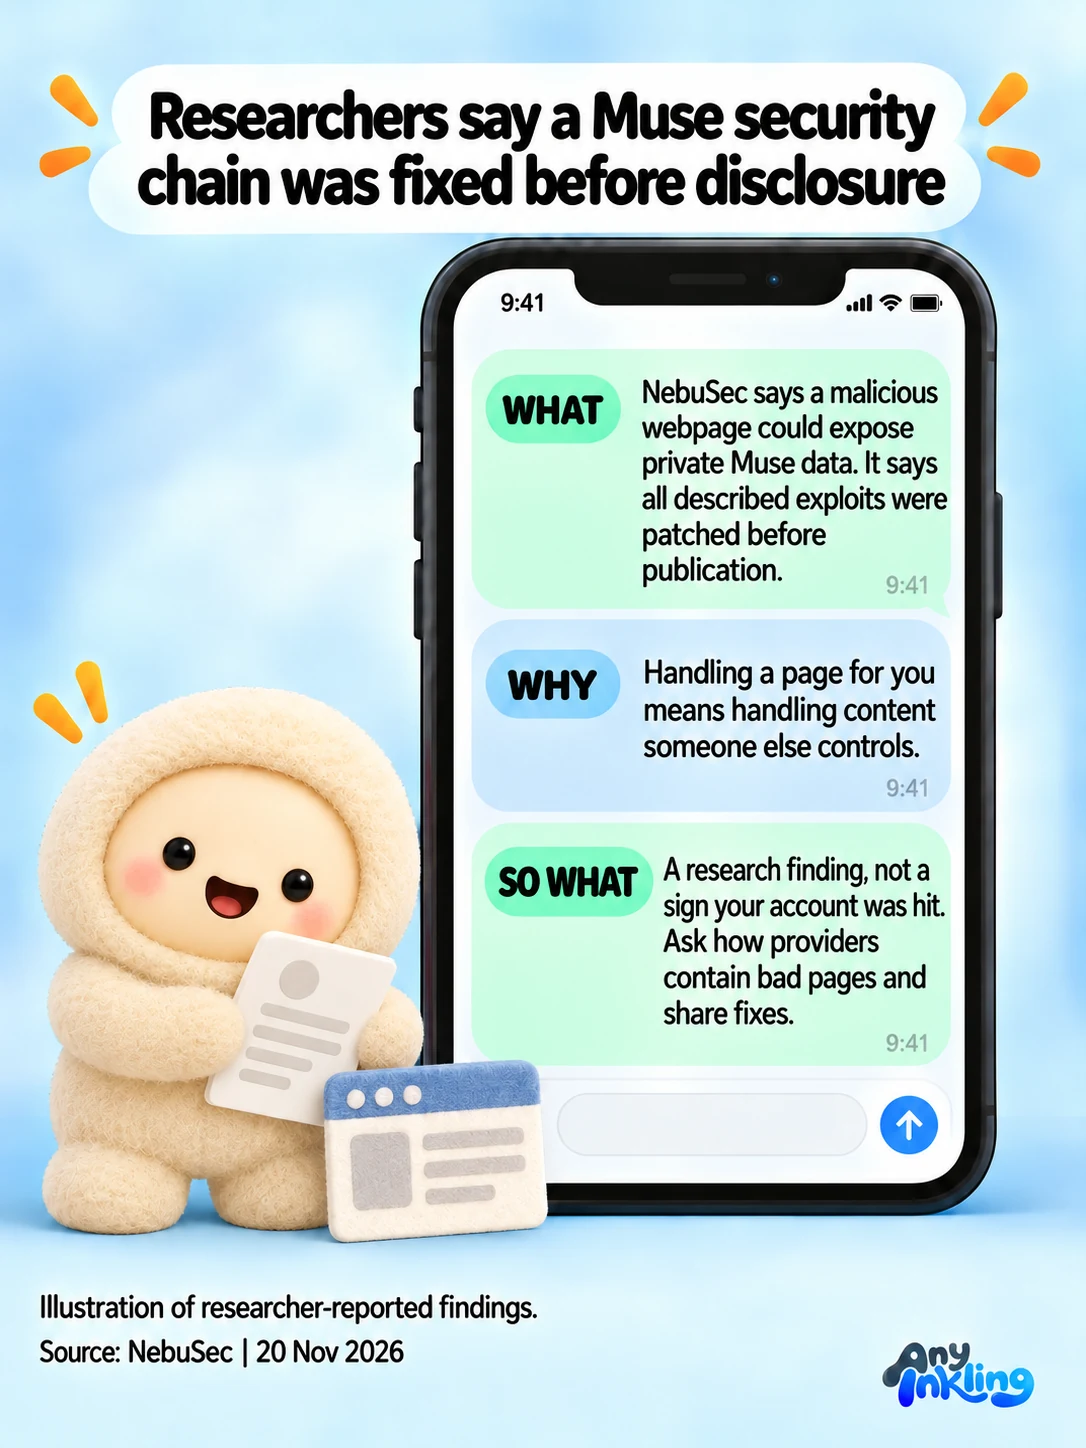
- NebuSec, a security research firm, published a report on 20 November describing how an attacker-controlled webpage could expose private information inside a Muse user's environment. The researchers say all exploits described in the report were patched by the time of publication.
- In their demonstration, having Muse export a malicious webpage gave them a route to read conversation history and memories without triggering a network approval prompt. They also report being able to change stored context and reach protected credential storage.
- The researchers say the compromise stayed within one user's virtual machine. They say they did not demonstrate access to other users' environments or the underlying host.
- An assistant can handle an ordinary request, such as turning a webpage into a document, while meeting content someone else controls. This research is about why protecting the software that does that work matters alongside deciding what the assistant is allowed to do.
- A permission prompt is not the whole security boundary.
- Treat this as a research finding the researchers say was fixed, not evidence that your own account was affected.
- If you are choosing an assistant for sensitive work, a useful question is how the provider contains malicious content and communicates fixes, rather than only whether it asks before sending something.
Generated editorial infographic. Illustration of researcher-reported findings, not our test.
Source: NebuSec describes its own research, and the findings and patch status are researcher-reported. We have not reproduced the chain or verified vendor fix dates or versions, and the report does not establish real-world exploitation.
NebuSec research report ↗
20 November 2026. Researcher report, not an Any Inkling test.